ARCHITECTURE · CYBERSECURITY · CRYPTOGRAPHY · COMPLIANCE

We protect what keeps your business running.

We reduce risk, complexity and compliance burden in critical operations. Then we translate that goal into architecture, controls, cryptography and evidence.

Less exposure. Less friction. More control.

PCI DSSISO 27001ISO 22301PRIVACYPOST-QUANTUMZERO TRUST
TECHNOLOGY DEVELOPED BY ZTC

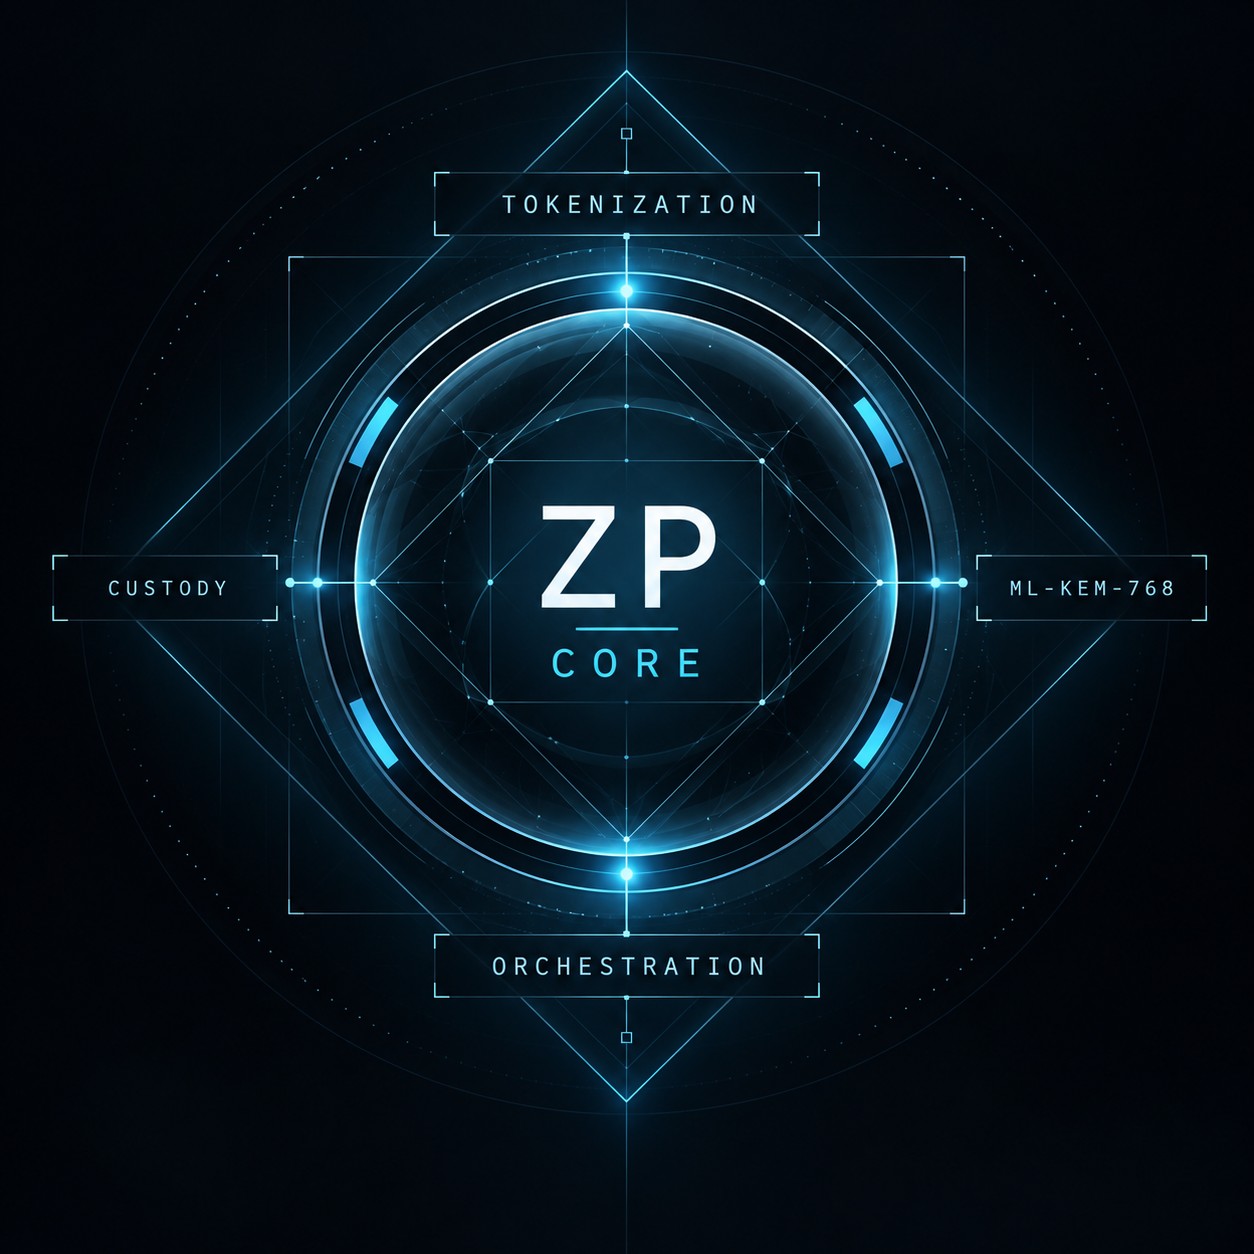
ZEROPAN CORE

The first Post-Quantum Cryptographic Vault in Mexico and Latin America.

Less exposure. Less complexity. More control over your payments.

ZEROPAN CORE cryptographic core

ZEROPAN CORE keeps payment card data outside business applications and lets them work with a secure reference —a token— instead of the full card number. This can reduce the number of systems handling sensitive data, simplify the PCI DSS environment and reduce dependence on a single vault or processor.

Reduce card-data exposureFewer applications and systems need to handle the full card number.
Reduce the PCI DSS burdenFewer systems handling card data can mean a smaller PCI environment, fewer controls to manage and less evidence to maintain.
Keep greater controlYour business keeps a secure reference —a token— while sensitive card data remains protected in ZEROPAN CORE.
Explore ZEROPAN CORE ↗
01CAPTURE

The customer registers the card securely.

02PROTECTION

ZEROPAN safeguards the full card number.

03TOKEN

Your application receives a secure reference, not the sensitive data.

04PAYMENT

A compatible processor executes the payment.

01
PRIMARY OUTCOME

Reduce exposure and the PCI DSS burden

A properly designed integration can keep the full card number —Primary Account Number (PAN)— and security code (CVV) out of business systems, reduce in-scope components and make controls, evidence and audits easier to manage.

Final scope reduction depends on the architecture and applicable validation.
02

Protect and control card data

Your business operates with a secure reference while ZEROPAN CORE concentrates protection and control of sensitive card data.

03

Reduce processor dependency

Separating custody from processing makes it easier to evolve integrations, acquirers or compatible processors without rebuilding the entire business logic.

04

Prepare for cryptographic evolution

The architecture uses ML-KEM-768 in specific components and a crypto-agile design that can evolve as post-quantum standards change.

CHALLENGES WE SOLVE

Security that translates into business outcomes.

We help reduce risk, simplify compliance, protect critical information and prepare operations for technology shifts that are already reshaping security.

PAYMENTS & COMPLIANCE

Reduce the burden of PCI DSS

We narrow scope, organize controls and evidence, and guide remediation so PCI becomes easier to manage.

PCI DSS 4.0.1 · Scope · Gap · Evidence · Readiness →
RISK

Understand and reduce risk

We translate technical scenarios into impact, priorities and decisions management and boards can act on.

Risk Assessment · ISO 31000 · Treatment →
INFORMATION & PRIVACY

Protect information and privacy

We align governance, controls and evidence to protect sensitive information and meet security and privacy obligations.

ISO 27001 · Privacy · Governance · Evidence →
AUDIT & ASSURANCE

Prove controls work

We review controls, gaps and evidence before an auditor, regulator or third party finds the problem.

Audit · Assurance · Gap · Control Testing →
CONTINUITY & RESILIENCE

Keep the business running

We strengthen continuity and recovery so an incident does not become a prolonged business interruption.

ISO 22301 · Continuity · Resilience →
CRYPTOGRAPHIC EVOLUTION

Prepare for post-quantum cryptography

We identify dependencies and build an orderly transition before the change becomes urgent.

PQC · Crypto-agility · Inventory · Roadmap →
EXTERNAL EXPOSURE

See what the internet exposes

We detect signals of impersonation, fraud and external exposure before they escalate.

Digital Risk · OSINT · Fraud · Impersonation →
TECHNICAL VALIDATION

Validate technically

When needed, we test applications, APIs, cloud and infrastructure to verify that controls are effective.

Security Testing · Pentest · APIs · Cloud →
WHO WE HELP

Organizations that cannot afford technology to fail.

Banks, fintechs, financial services and critical infrastructure — but also any organization whose operations, revenue, customer service or continuity depend on digital platforms.

01

Banking

Payments, privacy, continuity, cryptography and compliance in regulated environments.

PCI DSS · ISO 27001 · PRIVACY · RESILIENCE
02

Financial services

Risk, information security, continuity and evidence for business decisions.

RISK · ISO 27001 · ISO 22301 · ASSURANCE
03

Fintech

Cloud, payments, fraud, privacy and growth with verifiable controls.

CLOUD · PAYMENTS · PRIVACY
04

Acquirers & PSPs

Card data, tokenization, PCI DSS and payment architecture.

TOKENIZATION · PCI DSS · CARD DATA
05

Payment processors

CDE, cryptography, tokenization, evidence and operational continuity.

CDE · CRYPTOGRAPHY · RESILIENCE
06

Critical infrastructure

Zero Trust, continuity, recovery and resilience for essential capabilities.

ZERO TRUST · ISO 22301 · CONTINUITY
07

Telecommunications

Identity, availability, cloud and digital exposure at scale.

IDENTITY · CLOUD · DIGITAL RISK
08

Digital operations

Any company that depends on applications, cloud, data or digital platforms to operate, sell or serve customers.

CLOUD · PRIVACY · RESILIENCE · CYBERSECURITY
HOW WE WORK

From problem to evidence.

We define the context, understand the risk, intervene where it matters, and leave a result that can be verified.

01UNDERSTAND

Context, scope and business objective.

02PRIORITIZE

Risk, dependencies and critical decisions.

03INTERVENE

Architecture, controls, remediation or validation.

04DEMONSTRATE

Evidence, traceability and next step.

ONE CONCRETE PROBLEM · ONE NEXT STEP

Tell us what you need to protect, demonstrate or transform.

We can start by defining the problem before discussing a solution.

Talk to ZTC ↗